Planning Emergency Lockdown with Access Control
Plan commercial lockdown door states, authority, communications, safe egress, testing and recovery before selecting access-control automation.
When a serious threat is reported, customers want the right areas secured quickly while occupants can still follow the approved safety plan and emergency responders can enter where intended. A generic “lock every door” command cannot prove that result. It may change the wrong openings, conflict with another emergency sequence or leave staff uncertain about who can act.
The practical approach is to define each emergency scenario, assign every affected door an intended state, name the people authorized to initiate and release it, and witness the complete response before relying on automation. Keep an adequate existing system or a clear manual procedure when it passes the same tests and further automation would add little value. Have the responsible safety, fire, building, accessibility and security parties approve decisions within their authority.
Which customer outcome should the lockdown plan deliver?
The customer is buying a coordinated emergency response. A software button is one component. Access control can change door states and record actions. The organization still needs a site-specific plan that tells people what the alert means and what they should do.
Start with a short outcome statement for each credible scenario. For example:
- authorized staff can rapidly restrict entry at selected perimeter doors when a threat is outside;
- occupants can move to identified secure areas when the approved plan calls for internal refuge;
- people can still use the required egress route if conditions require evacuation;
- emergency responders can enter through an agreed route without searching for an unavailable employee; and
- authorized leadership can confirm the all-clear, return doors to normal and account for exceptions.
These planning examples require adaptation. Threat location, building use, occupancy, door hardware and emergency-service direction can change the appropriate response.
The City of Toronto’s Lockdown Procedures distinguish responses such as shelter in place, hold and secure, and full lockdown. The policy recommends site-specific procedures based on a workplace violence risk assessment, effective staff communication, practice and preservation of the ability to evacuate when circumstances require it. It is a City workplace policy, last reviewed by its committee in 2016 and modified online in 2026. A private commercial property should use it as a planning reference and develop its own approved procedure.
Is lockdown the right response to the identified concern?
Use the workplace risk assessment and emergency plan to decide which scenarios deserve a lockdown response. A technology purchase should not create a new emergency procedure without that operational foundation.
Ontario’s Occupational Health and Safety Act requires employers to assess workplace-violence risks arising from the nature, type and conditions of the workplace. The workplace-violence program must include measures and procedures to control identified risks likely to expose a worker to physical injury, summon immediate assistance, report incidents and explain how the employer will investigate and deal with them. The Act does not prescribe a lockdown button or one door sequence for every workplace.
Ask these questions before changing hardware:
- What situation is the procedure designed to address?
- Is the threat expected outside, inside or unknown?
- Who is present during normal, public, delivery and after-hours periods?
- Where can occupants receive reliable instructions or take approved refuge?
- Which doors would help the response if their state changed?
- Which doors must preserve an approved fire, egress, accessibility or operational function?
- Who summons police, fire or medical assistance, and through which independent method?
A site may need more than one response. It may also find that staff communication, reception procedures, door maintenance or a revised emergency plan addresses the immediate gap without a major access-control upgrade.
What can go wrong when door behaviour is left undefined?
Undefined door logic can turn a helpful feature into a new source of uncertainty. The following illustrative failure cases are test prompts; no frequency is implied:
- a perimeter entrance remains on a daytime-unlock schedule after the emergency command;
- an interior door secures in a direction that prevents the movement expected by the safety plan;
- staff hear “lockdown” and remain unsure whether the concern is outside or inside;
- a physical input changes doors without giving the initiator clear confirmation;
- a cloud, network, controller or power interruption produces an undocumented state;
- a responder route is secured and no authorized person is available to release it;
- two active scenarios issue conflicting commands to the same door; or
- the emergency is released in software while one opening remains mechanically or electrically abnormal.
Current public discussions among access-control technicians and employees raise questions about these exact subjects, including selective door groups, fire-alarm behaviour, false activation, release authority and forgotten restoration. Their evidentiary role is limited to question discovery. Authoritative sources and building-specific review must establish technical facts and legal requirements. The available discussions provide no defensible estimate of failure frequency. The design and test plan must resolve each issue for the actual property.
How do you create a scenario-to-door-state matrix?
Give every controlled opening a stable identifier and write its intended behaviour for each approved scenario. Avoid commands such as “secure the building” until the team has defined what that means at every door.
| Field | Decision to record |
|---|---|
| Door and location | Stable identifier, floor, zone and opening description |
| Normal state | Scheduled, credential-controlled, monitored, held open or another approved state |
| Scenario command | Lock, unlock, remain unchanged or follow another approved system sequence |
| Entry from unsecured side | Which credentials or roles remain valid, if any |
| Exit from secured side | Mechanical and electrical operation occupants will use |
| Fire and life-safety relationship | Approved release, recall, smoke-control or other interface behaviour |
| Power and communications loss | Expected state during controller, network, Internet and power failures |
| Responder access | Agreed entry route, key or credential custody and backup method |
| Status evidence | Position, lock, request-to-exit, fault and command feedback available to authorized staff |
| Recovery | Authorized release method and physical check needed before returning to normal |
Review vestibules, gates, elevator interfaces, loading entrances, tenant doors, automatic operators and fire separations as complete assemblies. A door can be physically open even when software reports that its lock command is secure. Position and lock monitoring answer different questions.
The 2024 RCMP Access Management Guide describes access management as a combination of hardware and standard operating procedures. It calls for defined staff responsibilities and includes lockdown and shelter-in-place among the emergency situations that security personnel may need to address. This guidance governs federal departments and agencies, so commercial teams should use its operating principles only where they fit their own risks and obligations.
How should safe egress constrain the access-control design?
Treat entry control and exiting as separate functions. A lockdown decision cannot be allowed to improvise the operation of an exit or access-to-exit door.
Ontario’s current Fire Code, O. Reg. 213/07 states, subject to its specified exceptions, that required exit doors and certain doors in access-to-exit routes must be readily openable from the inside with no more than one releasing operation and without keys, special devices or specialized knowledge. It also sets conditions for electromagnetic locking devices and requires periodic checks of specified egress-door features.
Application depends on the building, occupancy, approved design, hardware and current law. Ask the qualified design and service parties, and the authority having jurisdiction where required, to confirm each affected opening. Record:
- the latch, lock, closer, panic or exit hardware and door operator;
- the normal entry and exit sequence;
- the fire-alarm and emergency-release interfaces;
- power-loss behaviour and backup-power duration;
- accessible approach, operating force and activation needs;
- which components are listed or approved for the intended use; and
- the inspection and testing responsibility.
Test safe egress directly at the door under normal, lockdown, fire-alarm and approved failure conditions. Physical operation at the opening provides necessary evidence beyond a green icon on an access-control screen.
Who should be able to start, change or end a lockdown?
Authorize roles through the emergency plan, then configure the technology to support those roles. A broad administrator account or an unguarded button can create avoidable activation risk.
Define at least:
- the primary and backup people who may initiate each scenario;
- whether a person can act for one site, one zone or the full organization;
- who receives immediate notification and confirms that the command took effect;
- who may unlock a specific door during an active scenario;
- who accepts emergency-service direction;
- who may declare or confirm the all-clear; and
- who inspects the building and restores schedules, credentials and integrations.
Manufacturer documentation can reveal important implementation details. The customer’s authorized planning and safety parties approve the procedure. Verkada’s current Emergency Scenarios documentation, for example, allows a configured scenario to select doors that lock or unlock and assigns separate permissions to activate, release or unlock during the scenario. It also warns that multiple active scenarios can interact and that a lock command takes precedence for a door in its platform. This is one manufacturer’s current behaviour. Require the selected supplier to demonstrate the exact proposed version, licences, controllers, network path and door configuration.
For a physical initiation device, record its location, protective cover if used, accessibility, supervision, power, wiring path, labels, confirmation signal and cancellation method. Include accidental and malicious activation in the test plan. Keep a separate method for summoning immediate assistance because changing door states alone does not notify emergency responders.
What should staff, visitors and responders experience?
The alert must lead to a clear human action. A rapid door command offers little protection when occupants cannot distinguish the scenario or do not know where to go.
Build a communication matrix for employees, reception, contractors, visitors, tenants, people outside, people in common areas and people who need accessible assistance. For each group, define:
- the plain-language message they receive;
- the channel and backup channel;
- the action expected;
- where updated instructions come from;
- how hearing, vision, language, mobility and other accessibility needs are addressed; and
- what they do if the normal route, room or communication method is unavailable.
Coordinate responder access with the appropriate emergency services and property stakeholders. Avoid publishing sensitive access details in general staff material. Give the people who need them a controlled, current procedure.
Exercises should start with tabletop review and controlled functional testing. A live drill must be approved, communicated and designed to avoid trauma, unsafe movement or false emergency calls. Record questions and near misses without blaming participants. Confusion is evidence that the plan or training needs work.
What personal information should the system collect?
Lockdown systems may create cardholder events, mobile-app actions, door histories, acknowledgements and reports about who was present. Define the purpose of each record before using or retaining it.
The Office of the Privacy Commissioner of Canada’s Privacy in the Workplace guidance recommends limiting employee-information collection to identified purposes, providing transparency, restricting access on a need-to-know basis, applying safeguards and retaining information only as long as necessary for the stated purpose. Its discussion of employee information under PIPEDA directly applies to federally regulated employers. Other Ontario workplaces need to identify the laws, collective agreements and policies that govern their situation.
Ask the privacy and legal leads to decide:
- whether access events are used for emergency accountability and with what limitations;
- whether badge data can reliably show presence, given tailgating, missed reads and other gaps;
- who may view, export or disclose the event history;
- how long normal, test and incident records are retained;
- what the supplier and cloud providers can access;
- how employees are informed; and
- how records are preserved for an authorized investigation without creating indefinite retention.
Avoid quietly repurposing emergency or security records for attendance or performance monitoring. New uses require their own authority, necessity, transparency and proportionality review.
What belongs in a useful quote?
Ask suppliers to price one approved scenario matrix. A quote for “lockdown capability” is too vague to compare.
Cost and effort drivers can include:
- risk, emergency-planning and door-by-door design work;
- compatible controller capacity, inputs, relays and supervised wiring;
- lock, latch, closer, exit hardware, power supply and battery changes;
- fire-alarm, elevator, automatic-operator and notification interfaces;
- software editions, emergency-scenario licences and recurring services;
- physical buttons, protective devices and local confirmation indicators;
- network, identity, mobile-device and remote-access dependencies;
- drawings, permits, reviews and authority inspections where applicable;
- staff training, tabletop exercises and controlled drills;
- witnessed acceptance testing, deficiency correction and documentation; and
- recurring inspection, battery replacement, software support and retesting.
Request each inclusion, exclusion, assumption and recurring charge in writing. Ask what continues to work if Internet, cloud service, a controller, the fire alarm, building power or the supplier relationship is unavailable. A manual procedure may remain the most proportionate option for a small site when it is fast, accessible, practiced and verifiable.
Which acceptance tests prove the customer is ready?
Run tests with the facilities, safety, security, IT, property, door-hardware, fire-alarm and other responsible parties required for the affected systems. Protect normal operations and life-safety functions throughout.
| Test | Evidence of acceptance |
|---|---|
| Authorized initiation | Correct scenario starts through each approved primary and backup method |
| Unauthorized attempt | Unapproved user cannot initiate, release or override the scenario |
| Door-state result | Every affected opening reaches and reports its approved state |
| Occupant communication | Representative recipients receive and understand the correct message through primary and backup channels |
| Egress and emergency release | Each affected opening operates as approved under the applicable test conditions |
| Responder route | Agreed entry method works without exposing it to unauthorized users |
| Communications failure | Local or manual procedure remains understandable when a named dependency is unavailable |
| Power or controller failure | Doors, alerts and recovery match the approved failure sequence |
| Conflicting scenario | Precedence and operator information match the documented rule |
| Release and restoration | Authorized person ends the event, exceptions are inspected and normal schedules resume |
| Audit and privacy | Required actions are recorded, access is limited and retention is configured as approved |
Log the exact door, hardware, controller, software version, scenario, tester, expected result and observed result. Correct material failures and repeat the affected scenario plus related regression tests. Re-test after software upgrades, door changes, tenant reconfiguration, fire-system work or changes to the emergency plan.
What should the customer do next?
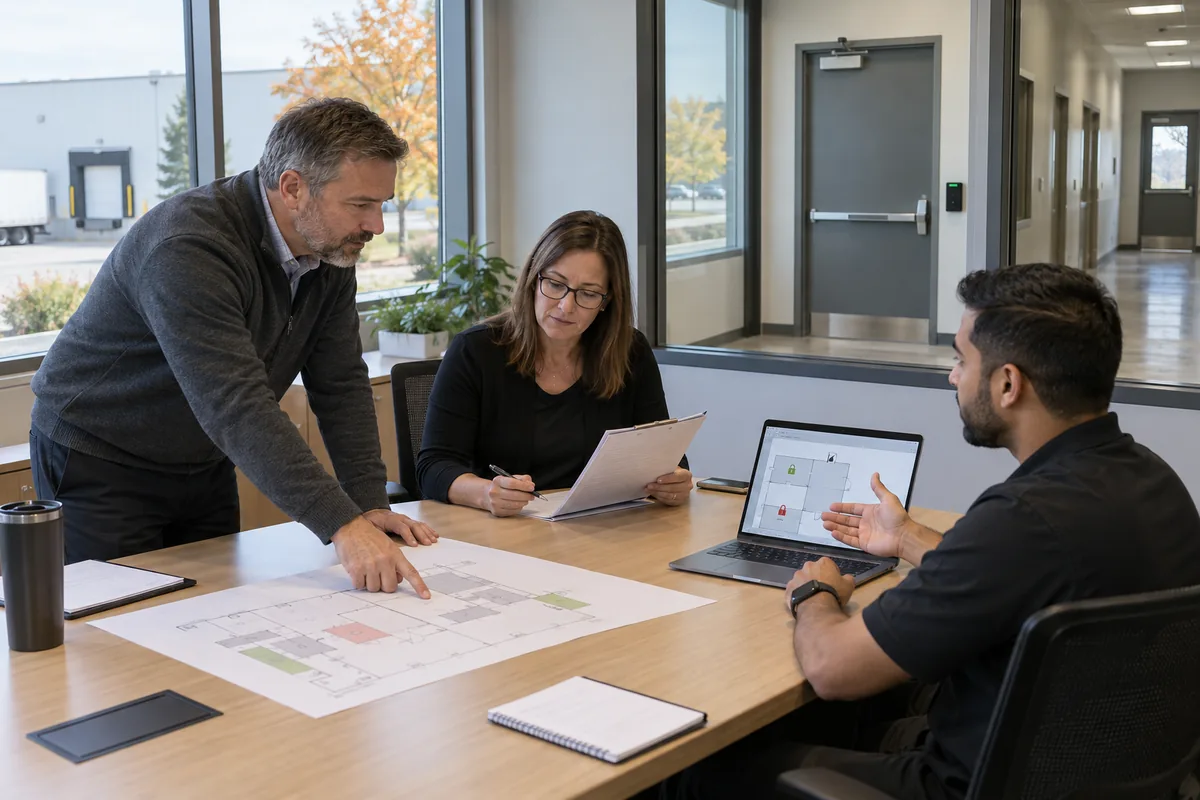
Begin with one facilitated tabletop session. Select the most credible scenario from the workplace risk assessment, mark every relevant opening on a current plan and complete the door-state matrix. Assign initiation, communication, responder and recovery roles. Then ask qualified parties to review the life-safety, accessibility and system interfaces before seeking comparable quotes.
Our commercial access-control service can help translate the approved procedure into a door-by-door design and witnessed test plan. The broader commercial security systems overview can help define how access control, alarms, video and operating responsibilities fit together.
Securitron Canada can help GTA organizations turn a lockdown objective into proportionate door logic, clear responsibilities and verifiable acceptance evidence.
Frequently Asked Questions
No universal all-door rule applies. The organization should define the threat scenario, occupant actions, required egress, responder access and the intended state of each affected opening. A qualified team must review the building-specific fire, building, accessibility and safety requirements before door logic is approved.
Approved egress and emergency-release functions must remain available as required for the building and opening. Entry restrictions and exiting are separate door functions. Confirm the applicable requirements, approved design and authority direction, then physically test every affected exit and access-to-exit door.
Assign named roles through the emergency plan and grant only the permissions each role needs. Define primary and backup initiators, release authority, exceptional door-unlock authority and the process for confirming an all-clear. Train and test those people under realistic conditions.
A physical input may improve speed and accessibility for some sites. It can also be pressed accidentally, become obstructed or depend on wiring and controllers. Compare it with supervised software, mobile and manual procedures. Test authorization, feedback, failure behaviour and cancellation for the selected method.
The test should prove that authorized people can initiate the correct scenario, each door reaches and reports its intended state, occupants receive clear instructions, approved egress and responder access remain available, failures are visible, and authorized staff can release the scenario and verify normal operation.